
Security requirements
Make device maintenance part of your resilience program
For financial entities subject to the EU's Digital Operational Resilience Act (DORA), device maintenance needs a clear operating process. Devicie helps IT and security maintain supported applications, manage agreed configuration and review reported results in an Intune environment.
Program and operations
Support operational resilience through everyday device management
DORA addresses digital operational resilience in the EU financial sector. Its scope includes ICT risk management, incident reporting, resilience testing and third-party risk. Device maintenance forms only part of that wider program.
Your organization needs to define the relevant requirements and connect them to the work its teams perform.
For supported devices managed through Intune, Devicie contributes application packaging, managed-policy drift correction and reporting. Evaluate those capabilities within your ICT risk-management processes and the responsibilities your organization retains.
Workflow by workflow
See how each workflow contributes
These are areas in which to evaluate a contribution. They do not represent a complete regulatory control mapping.
| Operational need | Devicie provides | Your team owns |
|---|---|---|
| Understand the supported device and application scope | Reported device information and installed application versions | Wider asset coverage, business dependencies, criticality and risk decisions |
| Maintain supported applications | Maintained catalog packages, submitted-installer packaging and reported installation results | Prioritization, rollout decisions, business acceptance and exceptions |
| Preserve agreed configuration | Drift correction for managed policies with readable notifications | Configuration requirements, authorization and formal change governance |
| Investigate maintenance results | Available device details, application results and policy-remediation notifications | Interpretation, follow-up, recordkeeping and the evidence required by your program |
Deliberate change
Keep deliberate changes controlled
A configuration change may be necessary to support a business requirement. Your teams need to establish who authorizes it, what is tested and how the result is reviewed.
Devicie supports a pause, edit and resume workflow for intentional changes to managed policies. When a managed policy drifts from its agreed state, Devicie corrects it and provides a readable notification.
Use those capabilities within your organization's change-management process. Establish the wider approvals, documentation and testing that your process requires.
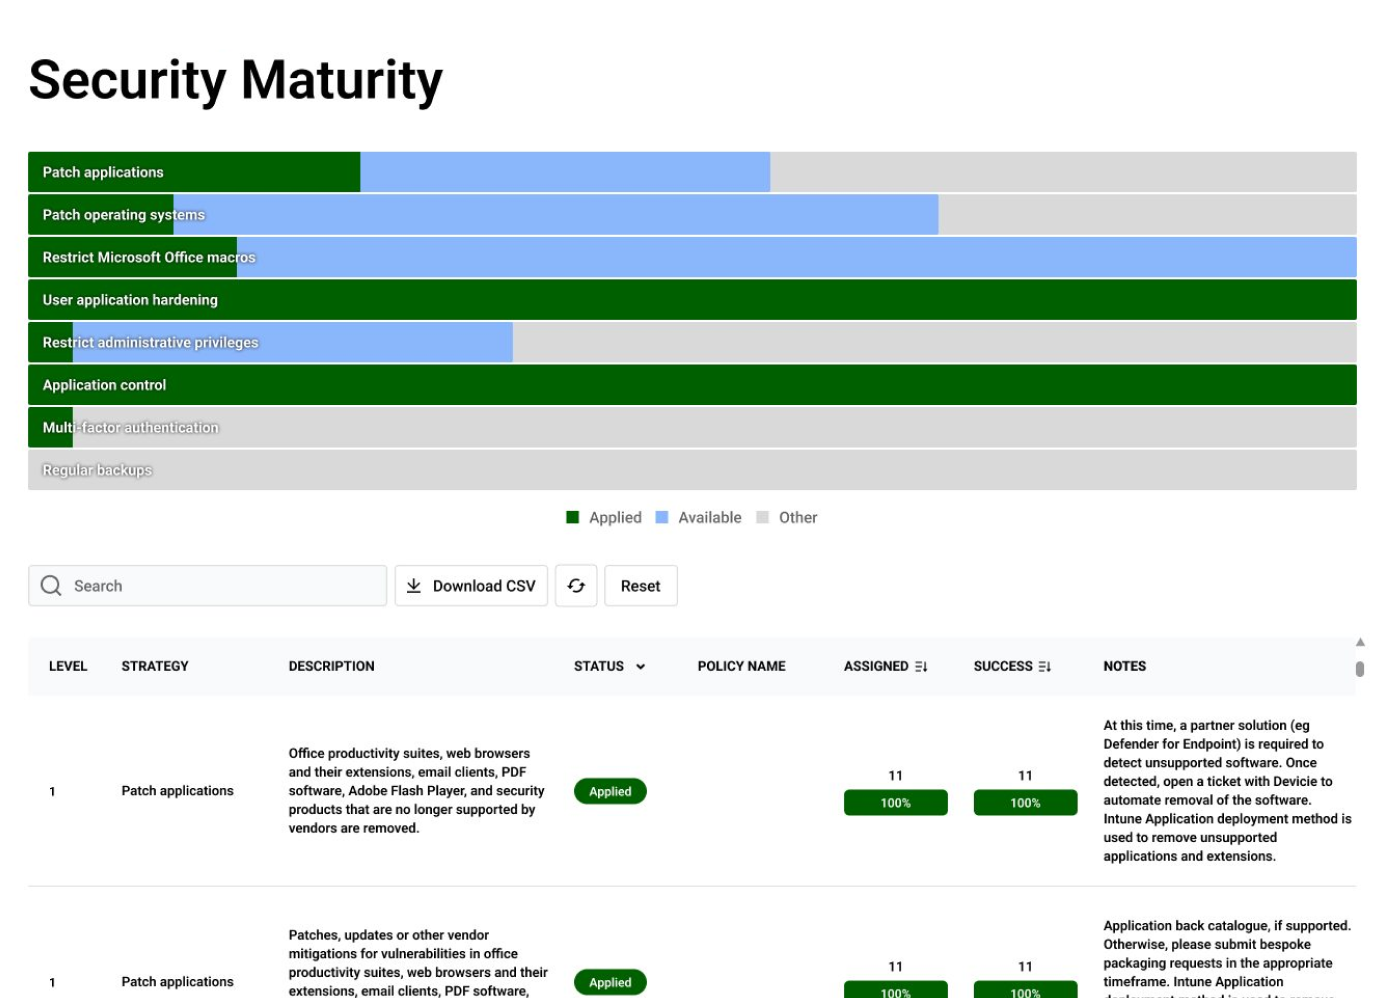
Reading the output
Review reported results alongside the activity
An available package shows that deployment preparation has reached a milestone. Reported installation results provide a different view of what happened on devices.
A policy-remediation notification shows that a managed policy was corrected. Its receipt by a device and effective device state need separate consideration.
Review those outputs with their scope and timing understood. Reporting refreshes daily. Your organization determines what additional records, retention and checks are necessary for its resilience program.
A shared review
Review results together across IT, security and risk
Choose a supported maintenance workflow and make the responsibilities explicit. Walk through the same application update or policy change together. Record what Devicie performs, what each team must decide and what additional records the program requires. That gives the broader resilience program a defined contribution from device operations, with organizational accountability retained.
IT
IT reviews package preparation, deployment and exceptions.
Security
Security reviews the agreed settings and maintenance priorities.
Risk and compliance
Risk and compliance owners assess how the process and available outputs fit the organization's obligations.
After implementation
Maintain the process after the initial implementation
Applications continue to release new versions. Administrators make changes. Business requirements evolve.
Devicie maintains catalog packages, corrects managed-policy drift and develops its configurations as Intune and security benchmarks change. Your teams can draw on that continuing work as they maintain and improve their environment.
Questions we get asked
Does Devicie make an organization DORA compliant?
No. Devicie supports specific device-management activities. DORA's wider requirements need an organization-wide implementation and evaluation against applicable obligations.
Is the reporting a complete DORA evidence repository?
The described reports and notifications can inform your reviews. Establish the additional records, retention, approvals and evidence your organization needs.
Does this cover incident reporting or resilience testing?
The workflows on this page concern application and configuration maintenance. Incident reporting and broader resilience testing require their own processes and capabilities.
What should we bring to a discussion?
A defined requirement, the supported devices or applications involved, and the process your team currently follows. That makes it possible to review the contribution and remaining responsibilities precisely.
Review a maintenance workflow against your requirements
Bring the relevant IT, security and risk stakeholders. Walk through an application update or a managed-policy change, inspect the reported output and discuss how it fits your program.